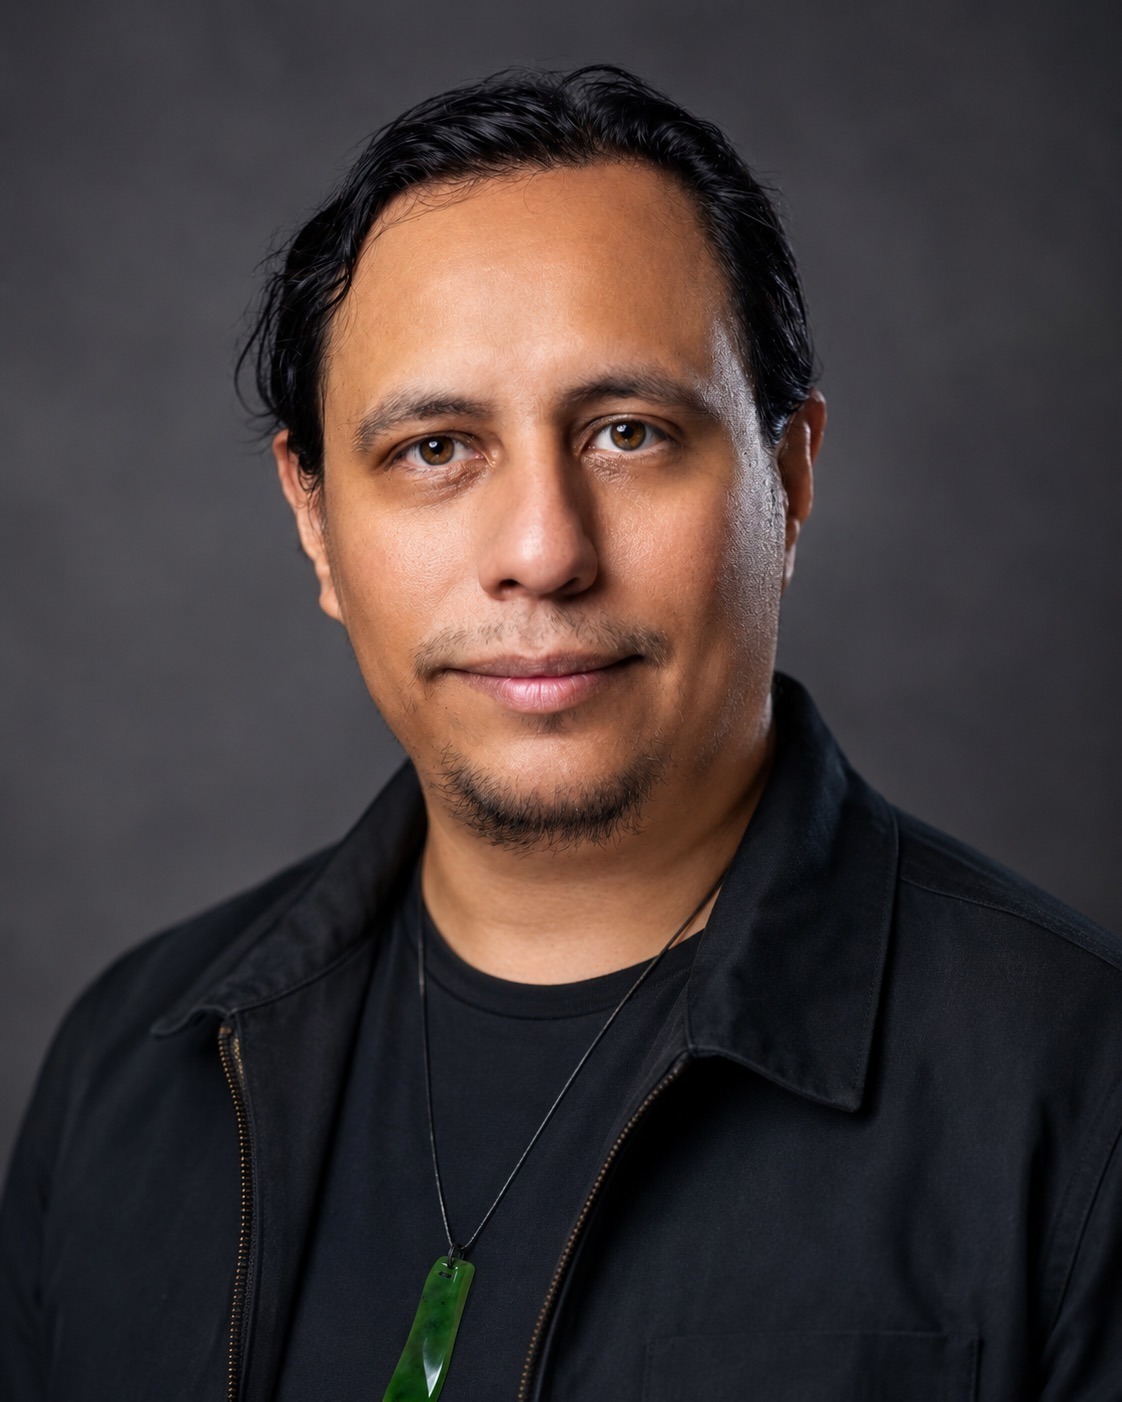
Frederick Kautz is an international AI, cybersecurity and technology professional and Leader. His work connects AI security, trusted infrastructure, and public policy. He co-authored NIST Special Publication 800-204D on software supply chain security, whose definition of the software supply chain was adopted by the U.S. Department of Defense. As co-creator of OmniBOR and protobom, he has helped build practical tools for understanding software dependencies and provenance. His work brings an engineering perspective to questions of institutional trust, technological dependence, and the security of interconnected systems.
Frederick co-founded MinIO and Network Service Mesh and held senior AI and engineering leadership roles at Elevance Health, where he helped shape enterprise Zero Trust strategy. He served as Co-Chair of KubeCon + CloudNativeCon and on the SPIFFE Steering Committee, and co-authored Solving the Bottom Turtle, a book on identity for software systems. His work on the Secure Agentic Framework (SAF) addresses threats and safeguards for AI agents. He brings the summit a practitioner’s perspective on translating security policy into controls that organizations can implement, verify, and sustain.